
London Headquarters & SOC
London Threat Command & 24/7 Operations
Continuous multi-sensor telemetry, Sigma correlation, and incident triage across UK-LON and European cloud fabrics.
Engineering deterministic cyber defense, autonomous AI governance, and Connected World resilience from our London Global Headquarters.

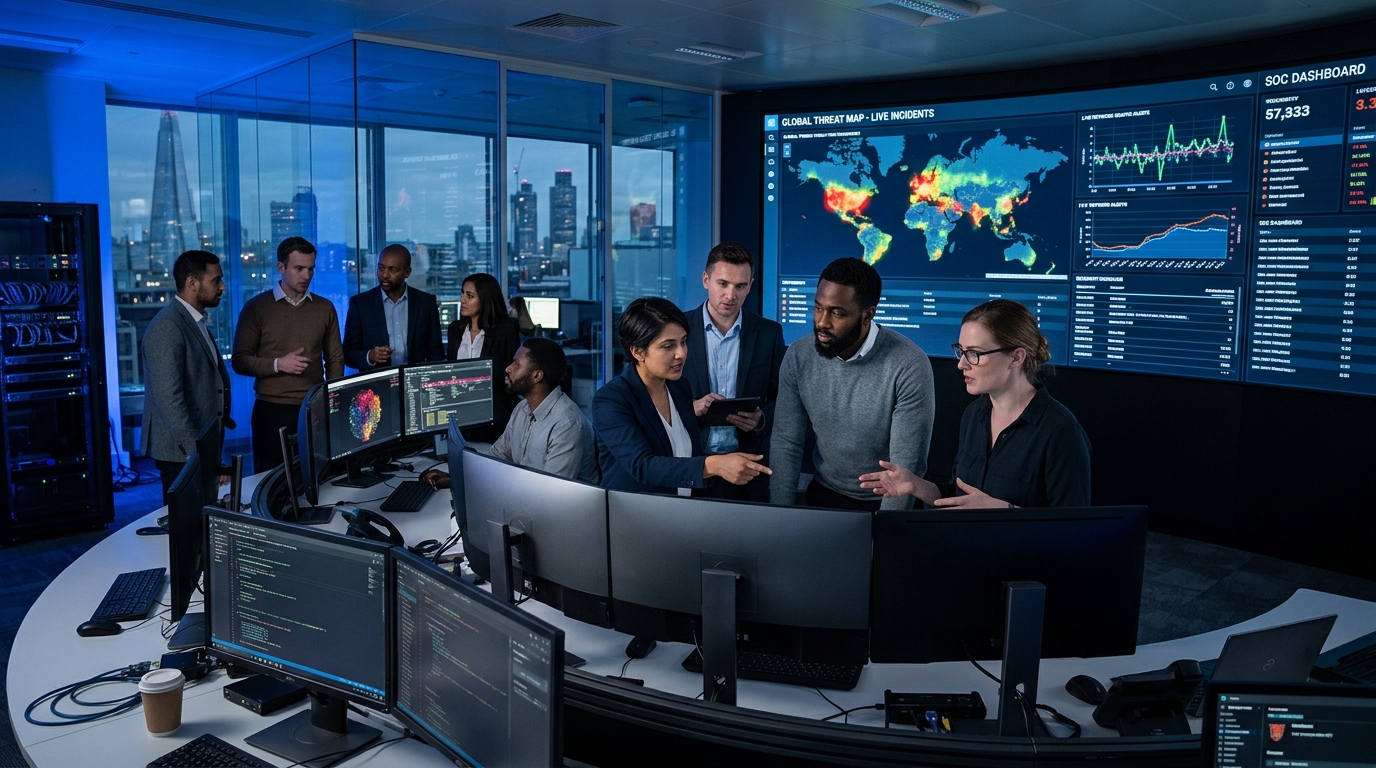
Cyber Security House is engineered and operated by ARYA AI TECHNOLOGY LTD (Company No. 17372232), registered in England and Wales. Positioned in London's financial and technology core, our operations center directs deterministic threat detection, autonomous AI governance, and Connected World resilience worldwide.
Operated by ARYA AI TECHNOLOGY LTD (Company No. 17372232) in London, United Kingdom, directing global cyber defense operations.
Senior defensive security architects, Sigma detection engineers, and AI safety researchers based in London.
Zero-trust HSM key vaults and PostgreSQL 16 FORCE RLS architectures strictly isolating customer telemetry in UK-LON, EU-FRA, MENA-RUH, and APAC-TYO.
24/7 incident triage enriched with ARYA SAI while all destructive remediation actions require named human sign-off.
Protecting smart homes, commercial buildings, EV charging networks, and industrial OT without invasive surveillance.
Continuous alignment with UK NCSC Cyber Essentials Plus, ISO/IEC 27001:2022, UK GDPR, and the UK NCSC 2028-2035 Post-Quantum roadmap.
Continuous multi-sensor telemetry, Sigma correlation, and incident triage across UK-LON and European cloud fabrics.

High-assurance encrypted data mesh interconnecting London, Frankfurt, Riyadh, and Tokyo sovereign operational clusters.
CSH-RULE-001..004) mapped to MITRE ATT&CK (T1110.001, T1098.003, T1048, T1190) with idempotent dedupe_key ingestion and SHA-256 immutable event hashes.[REDACTED_SECRET], [REDACTED_PII]), explicit per-agent Model Context Protocol (MCP) tool allowlists, and indirect prompt-injection blocking.ENABLE / FORCE ROW LEVEL SECURITY across all 20 tenant tables bound to transaction-local current_tenant_id(); cross-tenant queries fail closed with HTTP 403.isolate_host) and credential revocation require named human step-up approval recorded in an append-only audit trail.DNS TXT or HTTP ownership token required before scanning. Continuous evidence aligned with KISA 정보보호 및 개인정보보호 관리체계 (ISMS-P), 개인정보보호법 (PIPA), 국가정보원 양자내성암호 (KpqC).ML-KEM / ML-DSA), and 2035 full PQC completion.아니요. 탐지는 결정론적 규칙으로 수행되며 모든 격리 조치는 지정된 관리자의 승인이 필수입니다.
온보딩 시 영국(런던), 유럽(프랑크푸르트) 또는 엔터프라이즈 APAC 리전을 선택할 수 있습니다.
네, CSH Compliance가 기술적 증적을 ISMS-P, PIPA 및 ISO/IEC 27001 통제 항목에 지속 연결합니다.
DNS TXT 또는 HTTP 토큰으로 소유권을 증명한 자산만 스캔할 수 있습니다.
네, 위임 테넌트 관리와 라이선스 풀링을 지원합니다.
보안 엔지니어와 30분. 슬라이드 없이.