
London Headquarters & SOC
London Threat Command & 24/7 Operations
Continuous multi-sensor telemetry, Sigma correlation, and incident triage across UK-LON and European cloud fabrics.
Engineering deterministic cyber defense, autonomous AI governance, and Connected World resilience from our London Global Headquarters.

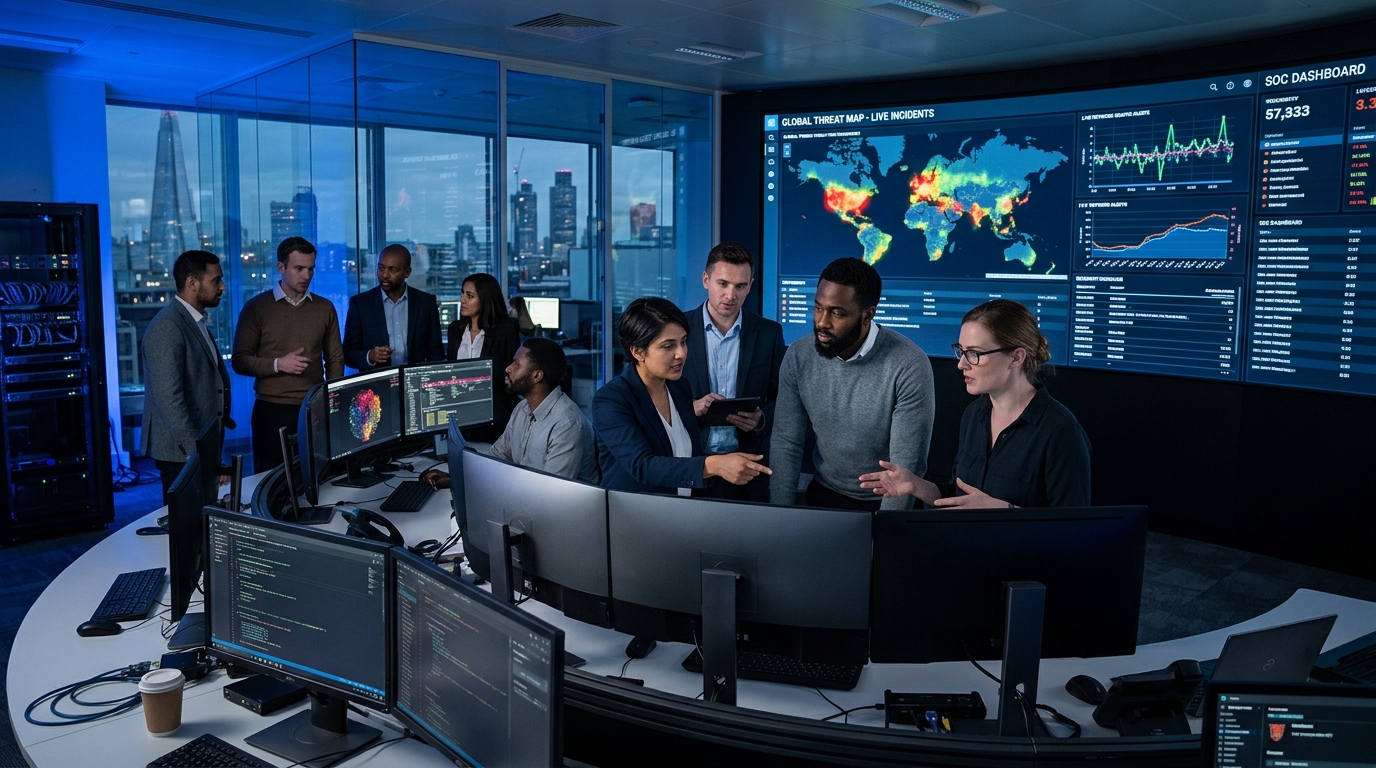
Cyber Security House is engineered and operated by ARYA AI TECHNOLOGY LTD (Company No. 17372232), registered in England and Wales. Positioned in London's financial and technology core, our operations center directs deterministic threat detection, autonomous AI governance, and Connected World resilience worldwide.
Operated by ARYA AI TECHNOLOGY LTD (Company No. 17372232) in London, United Kingdom, directing global cyber defense operations.
Senior defensive security architects, Sigma detection engineers, and AI safety researchers based in London.
Zero-trust HSM key vaults and PostgreSQL 16 FORCE RLS architectures strictly isolating customer telemetry in UK-LON, EU-FRA, MENA-RUH, and APAC-TYO.
24/7 incident triage enriched with ARYA SAI while all destructive remediation actions require named human sign-off.
Protecting smart homes, commercial buildings, EV charging networks, and industrial OT without invasive surveillance.
Continuous alignment with UK NCSC Cyber Essentials Plus, ISO/IEC 27001:2022, UK GDPR, and the UK NCSC 2028-2035 Post-Quantum roadmap.
Continuous multi-sensor telemetry, Sigma correlation, and incident triage across UK-LON and European cloud fabrics.

High-assurance encrypted data mesh interconnecting London, Frankfurt, Riyadh, and Tokyo sovereign operational clusters.
CSH-RULE-001..004) mapped to MITRE ATT&CK (T1110.001, T1098.003, T1048, T1190) with idempotent dedupe_key ingestion and SHA-256 immutable event hashes.[REDACTED_SECRET], [REDACTED_PII]), explicit per-agent Model Context Protocol (MCP) tool allowlists, and indirect prompt-injection blocking.ENABLE / FORCE ROW LEVEL SECURITY across all 20 tenant tables bound to transaction-local current_tenant_id(); cross-tenant queries fail closed with HTTP 403.isolate_host) and credential revocation require named human step-up approval recorded in an append-only audit trail.DNS TXT or HTTP ownership token required before scanning. Continuous evidence aligned with Esquema Nacional de Seguridad (ENS), INCIBE, Directiva NIS2 España.ML-KEM / ML-DSA), and 2035 full PQC completion.No. La detección se basa en reglas deterministas. ARYA SAI solo genera resúmenes consultivos sobre evidencia redactada y cada acción requiere aprobación humana.
Puede elegir residencia en la UE (Fráncfort) o Reino Unido (Londres) durante el alta.
Sí, CSH Compliance vincula evidencia técnica continua con los controles de ENS, NIS2, ISO/IEC 27001 y RGPD.
Solo activos cuya propiedad haya sido demostrada mediante token DNS TXT o HTTP.
Sí, ofrecemos gestión delegada de clientes y licencias agrupadas.
30 minutos con un ingeniero de seguridad. Sin diapositivas.