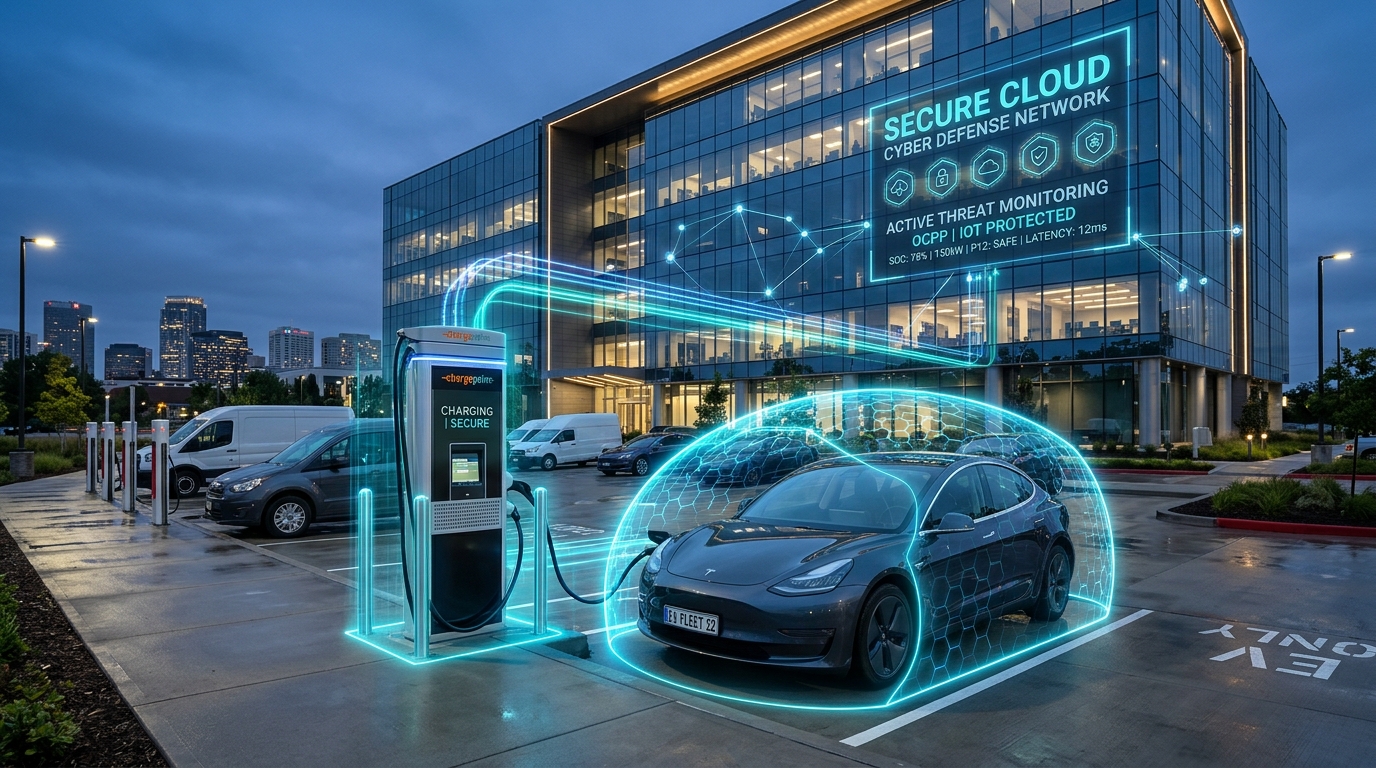
Visual Architecture
Read-Only OCPP 1.6J/2.0.1 Charging Security
Fleetwide ISO 15118 mTLS certificate lifecycle tracking and outage correlation with zero physical contactor actuation.
Read-only OCPP 2.0.1 charger posture, ISO 15118 certificate lifecycle and ISO/SAE 21434 awareness. (Volumi personalizzati, residenza dati UE/UK, SSO/SCIM e gestione multi-tenant delegata.)

Connects to authorised Charge Station Management Systems via read-only OCPP 1.6J Security Profile 3 and OCPP 2.0.1 feeds.
Tracks EVSE leaf certificates, TLS security profiles and impending expiry across depot and public charging fleets.
Monitors ISO 24089 / OCPP signed firmware update verification events and configuration drift.
Correlates charger outages with OCPP security events without falsely classifying utility grid faults as cyberattacks.
Policy EV-SAFE-001 blocks RemoteStopTransaction, current modification, contactor toggles and vehicle ECU/CAN commands with HTTP 403.
Supports operator readiness documentation without claiming accredited vehicle type approval.
Fleetwide ISO 15118 mTLS certificate lifecycle tracking and outage correlation with zero physical contactor actuation.
Specialist EV charging anomaly detection correlated with live regional power telemetry.
CSH-RULE-001..004) mapped to MITRE ATT&CK (T1110.001, T1098.003, T1048, T1190) with idempotent dedupe_key ingestion and SHA-256 immutable event hashes.[REDACTED_SECRET], [REDACTED_PII]), explicit per-agent Model Context Protocol (MCP) tool allowlists, and indirect prompt-injection blocking.ENABLE / FORCE ROW LEVEL SECURITY across all 20 tenant tables bound to transaction-local current_tenant_id(); cross-tenant queries fail closed with HTTP 403.isolate_host) and credential revocation require named human step-up approval recorded in an append-only audit trail.DNS TXT or HTTP ownership token required before scanning. Continuous evidence aligned with Agenzia per la Cybersicurezza Nazionale (ACN), Direttiva NIS2 Italia, GDPR.ML-KEM / ML-DSA), and 2035 full PQC completion.FORCE ROW LEVEL SECURITY on all 20 tenant tables.ALTER TABLE security_events ENABLE ROW LEVEL SECURITY; ALTER TABLE security_events FORCE ROW LEVEL SECURITY; CREATE POLICY tenant_isolation_policy ON security_events FOR ALL TO csh_app_role USING (organization_id = current_tenant_id()) WITH CHECK (organization_id = current_tenant_id());
No. Il rilevamento usa regole deterministiche. ARYA SAI produce solo riepiloghi consultivi e ogni contenimento richiede approvazione umana.
Scegliete tra UE (Francoforte) o Regno Unito (Londra) in fase di attivazione.
Sì, CSH Compliance collega automaticamente le prove tecniche ai controlli ISO/IEC 27001:2022, NIS2 e GDPR.
Solo gli asset di cui avete verificato la proprietà tramite DNS TXT o token HTTP.
Sì, con tenant delegati e licenze condivise.

30 minuti con un security engineer. Niente slide.